Kubernetes Security Best Practices for Production Clusters

Explore Kubernetes security best practices covering RBAC, pod hardening, network policies, secrets, supply chain protection, and runtime monitoring.
Key Takeaways
- Kubernetes Security Best Practices for Production Clusters.
- Explore Kubernetes security best practices covering RBAC, pod hardening, network policies, secrets, supply chain protection, and runtime monitoring.
- Kubernetes has become a cornerstone of modern application infrastructure.
Kubernetes has become a cornerstone of modern application infrastructure. Organizations use it to deploy microservices, manage containerized workloads, scale applications, and orchestrate complex cloud-native environments. However, as Kubernetes adoption grows, so does the responsibility to protect clusters, workloads, identities, and application data. A misconfigured cluster can expose sensitive information, allow unauthorized access, or provide attackers with a pathway into other systems. Furthermore, Kubernetes environments involve multiple interconnected components, including the API server, worker nodes, container images, network plugins, service accounts, and persistent storage. Each component introduces potential security risks. The good news is that Kubernetes provides several security mechanisms that help teams reduce these risks. By combining sensible configuration, automated controls, continuous monitoring, and disciplined operational practices, organizations can build a more resilient environment without creating unnecessary friction for developers. Understand the Kubernetes Security Landscape Before implementing security controls, understand what you need to protect. Kubernetes security extends beyond the cluster itself. It includes the application code, container images, infrastructure, deployment pipelines, identities, network traffic, and external dependencies that support your workloads. For example, an attacker might exploit a vulnerable application, steal a service account token, access the Kubernetes API, and attempt to move into other workloads. Alternatively, an exposed dashboard or overly permissive role could provide an easier entry point. Security therefore requires a layered approach rather than a single defensive mechanism. Start by identifying your critical assets and potential attack paths. Determine which workloads process sensitive information, which identities can modify cluster resources, and which systems can communicate with production services. Once you understand these relationships, you can prioritize controls according to risk rather than applying identical restrictions everywhere. Build a Secure Cluster From the Ground Up A secure Kubernetes deployment begins with its underlying infrastructure. Keep Kubernetes components and worker nodes updated, restrict administrative access, and avoid exposing control-plane endpoints directly to the public internet unless a carefully controlled architecture requires it. Managed Kubernetes services can reduce some operational responsibilities because the cloud provider manages portions of the control plane. However, managed services do not automatically secure application workloads, permissions, network policies, or container images. Your team must still configure these areas appropriately. Additionally, separate environments according to their risk and operational requirements. Development, testing, staging, and production workloads should not automatically share unrestricted access to the same resources. Depending on your isolation requirements, separate clusters may provide stronger boundaries than namespaces alone. Consider these foundational practices: Use private cluster endpoints where practical. Restrict access to control-plane interfaces. Harden worker-node operating systems. Disable unnecessary services and ports. Apply security updates promptly. Encrypt data in transit and at rest. Use dedicated identities for automation. Establish reliable backups and recovery procedures. A secure foundation reduces the number of weaknesses that application-level controls must compensate for later. Master Role-Based Access Control (RBAC) Role-Based Access Control, commonly known as RBAC, determines which users and service accounts can perform specific actions on Kubernetes resources. Poorly designed permissions can turn a small application compromise into a serious infrastructure incident. For instance, a workload that only needs to read configuration should not receive permission to create privileged pods, modify deployments across the cluster, or manage service accounts. Similarly, developers who deploy applications into one namespace may not need administrative access to every namespace. Use the principle of least privilege. Create Roles and RoleBindings for namespace-level access when possible, and reserve ClusterRoles and ClusterRoleBindings for genuinely cluster-wide requirements. Review permissions regularly as workloads and team responsibilities change. A simplified Role example looks like this: apiVersion: rbac.authorization.k8s.io/v1 kind: Role metadata: namespace: development name: pod-reader rules: - apiGroups: [""] resources: ["pods"] verbs: ["get", "list", "watch"] This role grants read access to pods within the specified namespace. It does not automatically grant permission to create, delete, or modify them. You can also inspect permissions using commands such as: kubectl auth can-i list pods \ --namespace development kubectl auth can-i create deployments \ --namespace development \ --as system:serviceaccount:development:app Avoid using the cluster-admin role as a convenient default. Although it simplifies troubleshooting, it also creates an unnecessarily large blast radius when credentials become compromised. Harden Containers and Container Images Container security starts before an image reaches the cluster. Every package, library, operating-system component, and executable included in an image can introduce vulnerabilities or unnecessary attack surface. Begin with trusted base images from reputable sources. Prefer minimal images that contain only the components required to run the application. Multi-stage Docker builds can help separate compilation dependencies from runtime dependencies, reducing the number of packages deployed into production. For example, a compiled application might use a full build environment during compilation but copy only the final executable into a smaller runtime image. This approach reduces image size and can simplify vulnerability management. Next, scan images for known vulnerabilities before deployment. Integrate scanning tools into CI/CD pipelines and establish policies for critical findings. However, do not rely exclusively on vulnerability scores. Consider whether a vulnerable component is reachable, whether a fix exists, and whether the affected workload is exposed. You should also: Pin images to immutable digests where practical. Remove unnecessary packages and debugging utilities. Avoid embedding credentials in image layers. Run containers as non-root users. Use read-only root filesystems when feasible. Drop unnecessary Linux capabilities. Sign images and verify provenance where supported. These practices reduce opportunities for attackers to exploit weaknesses inside running containers. Secure Pods With Pod Security Standards Kubernetes pods can request powerful operating-system capabilities. A container that runs as root, uses host networking, mounts sensitive host directories, or operates in privileged mode may undermine the isolation that containers are supposed to provide. Pod Security Standards define three security profiles: Privileged, Baseline, and Restricted. The Privileged profile allows broad capabilities, while Baseline prevents several known privilege-escalation patterns. Restricted applies stronger security requirements for workloads that can operate within those constraints. For most ordinary application workloads, aim for the Restricted profile where practical. Some applications require additional permissions, so evaluate exceptions carefully rather than disabling security controls across an entire cluster. A hardened pod specification might include settings such as: apiVersion: v1 kind: Pod metadata: name: secure-app namespace: production spec: automountServiceAccountToken: false securityContext: runAsNonRoot: true seccompProfile: type: RuntimeDefault containers: - name: app image: registry.example.com/app@sha256:REPLACE_WITH_DIGEST securityContext: allowPrivilegeEscalation: false readOnlyRootFilesystem: true capabilities: drop: - ALL Replace the example image digest with a valid, verified digest before deploying the manifest. Also ensure that the image supports non-root execution and that the application can operate with a read-only root filesystem. For namespace-level enforcement, administrators can use Pod Security Admission labels to establish appropriate security levels. Test policies against existing workloads before enforcing stricter requirements in production. Protect Secrets and Sensitive Configuration Applications often need database passwords, API tokens, signing keys, certificates, and other sensitive values. Unfortunately, developers sometimes place these values directly into container images, Git repositories, environment files, or deployment manifests. Avoid that practice. Hardcoded credentials can persist in repository history, image layers, build logs, and backups long after someone removes them from the current configuration. Kubernetes Secrets provide a standard mechanism for distributing sensitive values to workloads. However, creating a Secret does not automatically guarantee confidentiality. By default, Kubernetes Secret data is encoded using Base64, which is not encryption. Enable encryption at rest for Kubernetes data in etcd, restrict Secret access through RBAC, and use a managed key service or external secret-management platform where appropriate. Tools such as external secret operators can synchronize secrets from approved secret stores without requiring developers to manage long-lived credentials manually. Also consider how applications consume secrets. Mounting secrets as files can sometimes reduce accidental exposure through process listings or diagnostic output compared with environment variables, although neither approach eliminates all risks. Finally, rotate credentials regularly and immediately revoke any credential suspected of compromise. Secret management should cover the entire lifecycle, from creation and distribution to rotation and deletion. Strengthen Network Security With Network Policies By default, Kubernetes networking can allow pods to communicate with one another without restrictive network policies. This flexibility makes application deployment straightforward, but it can also create unnecessary pathways for lateral movement. NetworkPolicies allow you to control ingress and egress traffic for selected pods, provided your cluster networking implementation supports the relevant policy enforcement. For example, a frontend service may need to communicate with an API service, while the API service needs access to a database. Neither workload necessarily needs unrestricted access to every other pod. A practical approach begins with mapping application communication patterns. Identify required connections, then define policies that allow those connections while blocking unnecessary traffic. This is more reliable than guessing which ports a workload might need. Consider adopting a default-deny policy for ingress, egress, or both in suitable namespaces. However, test these policies carefully because indiscriminate egress restrictions can interrupt DNS resolution, external APIs, telemetry collection, and other essential functions. Network segmentation should complement identity controls and application-level authorization. NetworkPolicies limit connectivity, but they do not independently prove that a permitted request comes from a trusted user or application. Secure the Kubernetes API Server and Control Plane The Kubernetes API server is the primary interface for managing cluster resources. Because users, automation systems, and controllers rely on it, unauthorized API access can have serious consequences. Start by limiting which networks can reach the API server. Where supported, use private endpoints, approved IP ranges, or controlled access paths. Require authenticated access, enforce authorization, and avoid sharing administrative credentials between engineers or automation systems. Review API server configuration and audit settings according to your cluster distribution. Managed Kubernetes providers expose different configuration options, so the exact implementation will vary. Nevertheless, the underlying objective remains the same: limit access, record important actions, and reduce unnecessary privileges. Pay attention to service accounts and workload identity. Kubernetes workloads should not receive API access unless they need it. Set automountServiceAccountToken: false for workloads that do not require a token, and grant narrowly scoped permissions to those that do. Also protect etcd, which stores Kubernetes cluster state and may contain sensitive configuration. Restrict network access, protect backups, and ensure encryption requirements are satisfied. Control-plane security is not complete until stored cluster data receives appropriate protection. Protect the Software Supply Chain Kubernetes security depends on more than the cluster configuration. Applications arrive through a software supply chain that includes source repositories, dependencies, build systems, container registries, deployment manifests, and artifact promotion workflows. An attacker who compromises any of these components may introduce malicious code or alter deployment configuration before an application reaches production. Consequently, cluster hardening must extend into the build and release process. Begin by scanning application dependencies and infrastructure configuration. Use tools that identify vulnerable packages, exposed secrets, insecure container settings, and misconfigured Kubernetes manifests. Run these checks automatically during pull requests and before artifact promotion. Next, strengthen artifact integrity. Use trusted registries, immutable image references, digital signatures, and provenance verification where your environment supports them. Restrict who can publish production images and separate build permissions from deployment permissions. Software bills of materials can also help teams understand which dependencies an application contains. When a new vulnerability appears, an accurate inventory makes it easier to identify affected workloads and prioritize remediation. Ultimately, supply-chain security should make it difficult for an unapproved artifact to move from source code into production without the necessary validation. Implement Runtime Security and Threat Detection Preventive controls reduce risk, but they cannot eliminate every vulnerability or misconfiguration. Runtime security helps identify suspicious activity after workloads start executing. Monitor for unexpected process execution, unusual network connections, suspicious file changes, privilege escalation attempts, and activity involving sensitive system paths. Runtime security tools can use operating-system telemetry, container events, system calls, and behavioral rules to identify potentially malicious activity. For example, a web application that suddenly launches a shell, modifies system binaries, or attempts to access credentials outside its normal scope deserves investigation. Similarly, a workload that begins communicating with an unfamiliar external destination may indicate compromise or an application defect. Tools such as Falco can help detect suspicious runtime behavior through configurable rules. eBPF-based security platforms can provide additional visibility into process execution and network activity, depending on their capabilities and deployment configuration. However, avoid generating alerts for every unusual event without considering context. Excessive false positives can overwhelm engineers and cause genuine threats to go unnoticed. Tune detection rules, establish severity levels, and define response procedures before incidents occur. Secure Ingress, Service Meshes, and External Traffic Applications running in Kubernetes often expose services through ingress controllers, load balancers, gateways, or service meshes. These components create entry points that require careful configuration. Use TLS to protect traffic between clients and public-facing endpoints. Manage certificates through a trusted process, monitor expiration dates, and avoid disabling certificate verification to work around connectivity problems. Next, apply appropriate protections at the application edge. Depending on the architecture, these may include authentication, rate limiting, request-size limits, web application firewall rules, and protection against abusive traffic patterns. Internal traffic also deserves attention. Do not assume that communication between pods is automatically trustworthy simply because both workloads run inside the same cluster. Sensitive services should enforce appropriate authentication and authorization even when network segmentation is in place. A service mesh can help implement workload identity, mutual TLS, and traffic policies in supported architectures. Nevertheless, service meshes introduce additional operational complexity. Use them when their security and traffic-management benefits justify the additional components and maintenance requirements. Monitor, Audit, and Respond to Security Events Security controls are only useful when teams can determine whether they work and investigate when something goes wrong. Therefore, centralized logging, Kubernetes audit records, infrastructure monitoring, and incident-response procedures should form part of the security architecture. Kubernetes audit logs can record requests made to the API server, including information about the actor, operation, resource, and outcome. These records help investigators understand whether someone changed a privileged workload, modified an RBAC binding, or accessed a sensitive resource. Send relevant logs to a protected, centralized system. Restrict access to audit records and establish retention periods that match operational and regulatory requirements. Avoid storing sensitive application payloads or credentials in logs unnecessarily. Additionally, create alerts for high-risk events. Examples include unexpected privilege escalation, creation of privileged pods, changes to cluster-wide permissions, unusual access to Secrets, and modifications to security policies. Most importantly, prepare a response plan. When a workload appears compromised, teams should know how to isolate it, preserve evidence, revoke credentials, identify affected resources, and restore a trusted application version. Practicing these steps before a real incident reduces confusion under pressure. Automate Security With Policy as Code Manual security reviews become difficult to sustain as the number of clusters, teams, and deployments increases. Policy as code helps organizations define security requirements in machine-readable form and enforce them consistently. For example, a policy might reject workloads that run as root, use unapproved registries, omit required resource limits, or request privileged access without an approved exception. Tools such as Kyverno and Open Policy Agent with Gatekeeper can enforce policies through Kubernetes admission controls. These controls can prevent noncompliant resources from entering the cluster, rather than relying entirely on post-deployment discovery. However, policy enforcement requires careful rollout. Begin with audit or warning modes where supported, identify existing violations, and work with application teams to remediate them. Once the policies behave as expected, introduce enforcement gradually. Maintain policies in version control, review changes through pull requests, and test them against representative manifests. Treat security policy changes like software changes because an incorrect policy can block deployments or create unexpected gaps. Manage Vulnerabilities and Kubernetes Upgrades Kubernetes and its surrounding ecosystem evolve rapidly. New vulnerabilities emerge in operating systems, container runtimes, application dependencies, networking components, and Kubernetes itself. Establish a regular process for identifying vulnerabilities, evaluating their impact, prioritizing fixes, and verifying remediation. Critical vulnerabilities affecting exposed or privileged components may require immediate attention, while lower-risk findings can follow a planned maintenance schedule. Keep supported Kubernetes versions, node operating systems, container runtimes, and cluster add-ons up to date. Before upgrading production clusters, review compatibility requirements, test workloads in a representative environment, and confirm that backups and recovery procedures work. Avoid postponing upgrades indefinitely because they appear inconvenient. Unsupported versions may no longer receive security fixes, leaving the organization exposed to known weaknesses. Also review third-party controllers, Helm charts, operators, and network plugins. These components can introduce vulnerabilities even when the Kubernetes control plane itself remains current. Create a Secure CI/CD Pipeline for Kubernetes The deployment pipeline determines which code and configuration reach your cluster. If the pipeline is poorly protected, attackers may bypass otherwise strong cluster controls by publishing malicious images or modifying deployment manifests. Secure source repositories with appropriate access controls, branch protections, code reviews, and secret scanning. Then integrate automated tests, dependency analysis, image scanning, and infrastructure policy validation into the build process. Use short-lived credentials where supported and limit pipeline permissions to the resources required for each job. A build process that compiles application code should not automatically receive unrestricted production cluster administration privileges. Separate artifact creation from production deployment when practical. For instance, one pipeline can build and scan an image, publish it to a registry, and record its digest. A controlled deployment workflow can then verify the approved artifact before releasing it. Finally, monitor deployment failures and security-gate results. If developers repeatedly bypass controls because they are slow or unreliable, improve the workflow instead of weakening the security requirements without analysis. Common Kubernetes Security Mistakes to Avoid Some Kubernetes security failures arise from complex vulnerabilities. Others come from ordinary configuration shortcuts. Running every container as root, granting cluster-admin permissions for convenience, exposing the API server publicly, and storing credentials in repositories can create substantial risk. Another common mistake is assuming that namespaces provide complete security isolation. Namespaces help organize and isolate resources, but they do not independently enforce every network, identity, or infrastructure boundary. High-risk workloads may require additional controls or separate clusters. Teams also sometimes install security tools without establishing ownership for their alerts. A scanner that produces hundreds of findings each day provides limited protection if nobody triages the results or tracks remediation. Finally, avoid treating compliance as a one-time checklist. A cluster that passed a security review last quarter may contain new workloads, changed permissions, outdated images, or recently introduced vulnerabilities today. Build repeatable checks into daily engineering workflows. That makes security more dependable and reduces the burden of emergency remediation. Build a Practical Kubernetes Security Checklist A practical checklist helps platform teams translate security principles into repeatable operational tasks. Use it during cluster provisioning, application onboarding, deployment reviews, and periodic security assessments. Cluster and control plane Restrict API server access. Keep Kubernetes versions supported and updated. Protect etcd data and backups. Enable appropriate audit logging. Harden worker nodes and runtime configuration. Identity and access Apply least-privilege RBAC. Avoid shared administrative accounts. Disable unnecessary service account token mounting. Review permissions periodically. Use short-lived credentials where practical. Workloads and images Use trusted, scanned container images. Prefer immutable image digests. Run as non-root wherever feasible. Drop unnecessary Linux capabilities. Apply Pod Security Standards. Restrict privileged containers and host access. Network and secrets Apply suitable NetworkPolicies. Encrypt traffic using TLS. Restrict Secret access. Enable encryption at rest. Rotate compromised or expired credentials. Delivery and operations Scan dependencies and infrastructure manifests. Verify artifact integrity and provenance. Enforce policies through automated controls. Monitor runtime activity. Maintain incident-response and recovery procedures. Review this checklist against your specific architecture rather than applying every control mechanically. Different workloads have different requirements, and some controls depend on the Kubernetes distribution or networking implementation. Make Security Part of Everyday Kubernetes Operations Kubernetes security is not a single configuration setting or a tool that can be installed and forgotten. It is a continuous discipline that spans infrastructure, identities, workloads, networks, software delivery, monitoring, and incident response. The strongest security strategies combine multiple layers. RBAC limits what identities can do. Pod Security Standards restrict dangerous workload configurations. NetworkPolicies reduce unnecessary connectivity. Secret-management systems protect credentials. Supply-chain controls verify artifacts, while runtime monitoring helps detect suspicious behavior. Automation makes these practices sustainable. Security policies, image scanning, vulnerability management, admission controls, and deployment validation can operate throughout the software lifecycle, helping teams identify problems before they become production incidents. Start with the highest-risk areas in your environment. Tighten permissions, harden workloads, protect secrets, and restrict network access. Then expand your controls through automated policy enforcement, continuous monitoring, and regular security reviews. Ultimately, the goal is not to make Kubernetes difficult to use. It is to create an environment where secure deployments become the natural path, unsafe shortcuts become harder to take, and engineering teams can deliver applications with greater confidence.
Read Complete Original Article
Published originally on HackerNoon
Related News
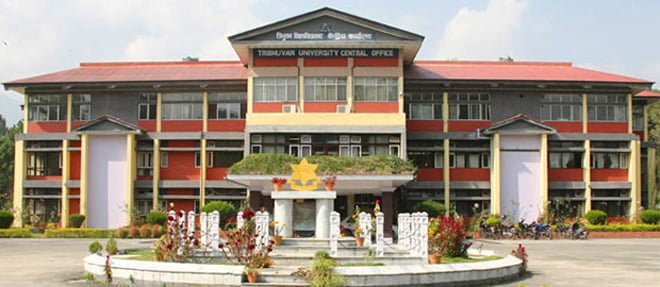
‘डिजिटल त्रिवि’देखि ‘रिसर्च युनिभर्सिटी’सम्मः के–के हुँदैछन् नयाँ काम?
त्रिभुवन विश्वविद्यालयले आफ्नो प्रशासनिक, शैक्षिक तथा प्राज्ञिक संरचनालाई समयानुकूल बनाउँदै डिजिटल सेवा विस्तार, अनुसन्धान प्रवर्द्धन, संस्थागत पुनःसंरचना र वित्तीय सुधारका नयाँ योजना अघि सारेको छ। त्रिविका सहकुलपति एवं शिक्षा तथा खेलकुदमन्त्री सस्मित पोखरेलको अध्यक्षतामा बसेको विश्वविद्यालय सभामा चालु आर्थिक वर्षको नीति तथा कार्यक्रम प्रस्तुत गरिएको थियो। यी योजना कार्यान्वयन भएमा विश्वविद्यालयको प्रशासनिक, शैक्षिक र प्राज्ञिक स्वरूपमा ठूलो फेरबदल आउने अपेक्षा गरिएको ...

इन्टरनेट प्याकेज र शुल्कमा प्राधिकरणको निगरानी, १४ सेवा प्रदायक कारबाहीमा
काठमाडौं । नेपाल दूरसञ्चार प्राधिकरणले स्वीकृत मापदण्ड र निर्देशनविपरीत इन्टरनेट सेवा सञ्चालन गरेको भन्दै १४ वटा इन्टरनेट सेवा प्रदायक कम्पनीलाई जनही ५० हजार रुपैयाँ जरिवाना गरेको छ ।प्राधिकरणले मंगलबार जारी गरेको प्रेस विज्ञप्तिअनुसार अनुमतिपत्रका सर्त उल्लङ्घन गरेको निरीक्षण तथा जाँचबुझबाट पुष्टि भएपछि दूरसञ्चार ऐन, २०५३ को दफा ४७ (१) बमोजिम कारबाही गरिएको हो ।प्राधिकरणका प्रवक्ता मिनप्रसाद अर्यालका अनुसार स्वीकृत प्याकेजअनुसार ...
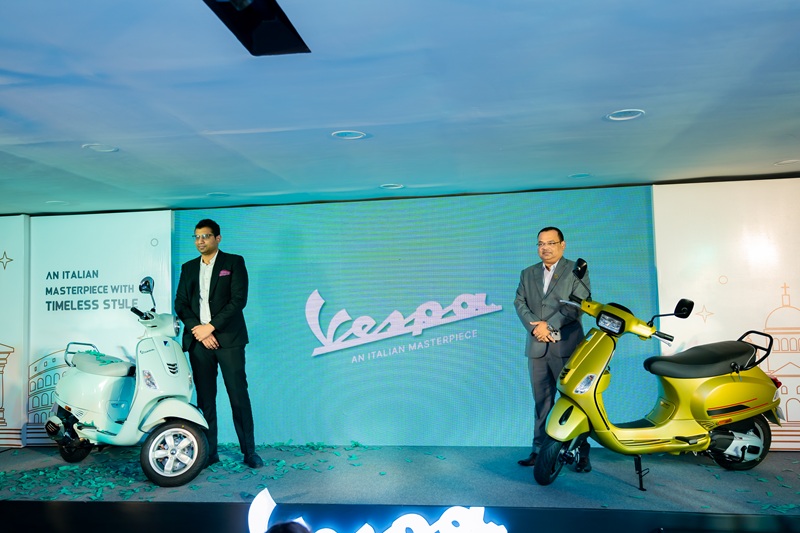
नेपालमा सार्वजनिक भयो भेस्पा १५० एफआई ओबीडी २ स्टेज बी: विशेषता तथा विवरण
२७ असोज, काठमाडौं। इटालियन स्कुटर ब्रान्ड भेस्पाले नेपाली बजारमा नयाँ १५० सिसी क्षमताको स्कुटर सार्वजनिक गरेको छ । नेपालका लागि भेस्पाको आधिकारिक वितरक डेल्टा अटोकर्प प्रालिले भेस्पा १५० एफआई ओबीडी २ स्टेज बी (Vespa 150 FI OBD 2 Stage B) सार्वजनिक गरेको हो । काठमाडौँको त्रिपुरेश्वरस्थित डेल्टा अटोकर्पको शोरुममा आयोजित विशेष कार्यक्रममार्फत नयाँ मोडल सार्वजनिक गरिएको […] The post नेपालमा सार्वजनिक ...
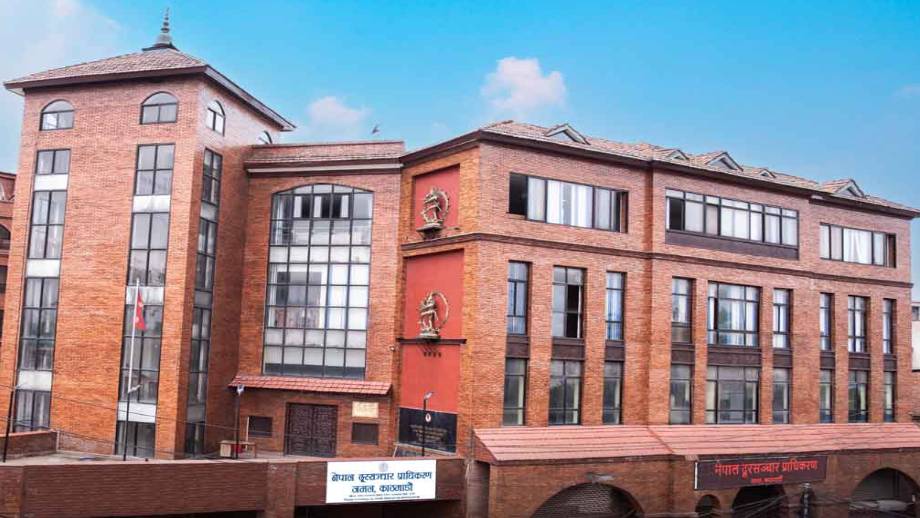
आफूखुशी शुल्क बढाउने १४ इन्टरनेट सेवा प्रदायकलाई प्राधिकरणले तिरायो जरिवाना, स्वीकृति नलिई लागू गरिएका प्याकेज र शुल्क तत्काल बन्द गर्न निर्देशन
नेपाल दूरसञ्चार प्राधिकरणले अनुमतिपत्रका शर्तविपरीत काम गरेको भन्दै १४ वटा इन्टरनेट सेवा प्रदायकलाई जनही ५० हजार रुपैयाँ जरिवाना गरेको छ। प्राधिकरणले आज एक विज्ञप्ति जारी गर्दै इन्टरनेट (इमेलसहित) सेवा सञ्चालन गर्न अनुमति पाएका सेवा प्रदायकले अनुमतिपत्रका सर्त तथा प्रचलित कानुनअनुसार सेवा सञ्चालन नगरेको निरीक्षण तथा जाँचबुझ प्रतिवेदनका आधारमा जरिवाना गर्ने निर्णय गरिएको जनाएको छ। दूरसञ्चार ऐन, २०५३ को दफा ४७(१) बमोजिम ती ...
All Information In One Place
Real-time headlines from trusted sources. Get the app now — stay updated, inspired, and ahead with breaking news!